Stan książek
Nasze książki są dokładnie sprawdzone i jasno określamy stan każdej z nich.

Nowa
Książka nowa.
Używany - jak nowa
Niezauważalne lub prawie niezauważalne ślady używania. Książkę ciężko odróżnić od nowej pozycji.
Używany - dobry
Normalne ślady używania wynikające z kartkowania podczas czytania, brak większych uszkodzeń lub zagięć.
Używany - widoczne ślady użytkowania
zagięte rogi, przyniszczona okładka, książka posiada wszystkie strony.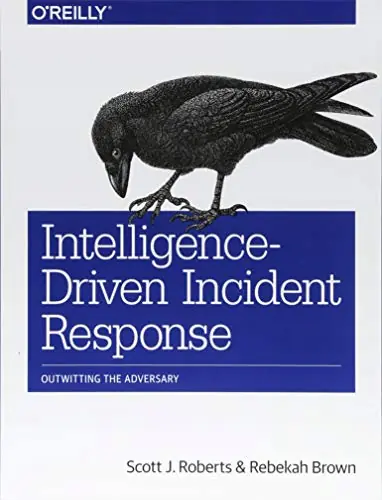
Scott Roberts IntelligenceDriven Incident Respo
Masz tę lub inne książki?
Sprzedaj je u nas

An effectively designed incident response plan is crucial when dealing with the aftermath of an online security breach. It allows your team to pinpoint attackers and understand their tactics. However, it's the application of a cyber threat intelligence mindset that unlocks the full potential of this information. This practical guide offers insights into the fundamentals of intelligence analysis and demonstrates how to integrate these techniques into your incident response strategy. Each approach strengthens the other: threat intelligence enhances incident response, while incident response creates valuable threat intelligence. This book is an essential resource for incident managers, malware analysts, reverse engineers, digital forensics experts, and intelligence analysts, offering guidance on how to leverage this symbiotic relationship effectively. The comprehensive text is structured into three parts: initially, it introduces the core concepts of cyber threat intelligence, the intelligence process, and the incident response process, illustrating how they interconnect. Then, it provides a practical walkthrough of the intelligence-driven incident response (IDIR) process, utilizing the F3EAD model—Find, Fix, Finish, Exploit, Analyze, and Disseminate. Finally, it examines broader aspects of IDIR, such as constructing intelligence teams, transcending individual incident-response cases.
Wybierz stan zużycia:
WIĘCEJ O SKALI
An effectively designed incident response plan is crucial when dealing with the aftermath of an online security breach. It allows your team to pinpoint attackers and understand their tactics. However, it's the application of a cyber threat intelligence mindset that unlocks the full potential of this information. This practical guide offers insights into the fundamentals of intelligence analysis and demonstrates how to integrate these techniques into your incident response strategy. Each approach strengthens the other: threat intelligence enhances incident response, while incident response creates valuable threat intelligence. This book is an essential resource for incident managers, malware analysts, reverse engineers, digital forensics experts, and intelligence analysts, offering guidance on how to leverage this symbiotic relationship effectively. The comprehensive text is structured into three parts: initially, it introduces the core concepts of cyber threat intelligence, the intelligence process, and the incident response process, illustrating how they interconnect. Then, it provides a practical walkthrough of the intelligence-driven incident response (IDIR) process, utilizing the F3EAD model—Find, Fix, Finish, Exploit, Analyze, and Disseminate. Finally, it examines broader aspects of IDIR, such as constructing intelligence teams, transcending individual incident-response cases.
Szczegóły
Inne książki tych autorów

Podobne produkty
Może Ci się spodobać
Inne książki z tej samej kategorii

Napisz opinię o książce i wygraj nagrodę!
W każdym miesiącu wybieramy najlepsze opinie i nagradzamy recenzentów.
Dowiedz się więcejWartość nagród w tym miesiącu
880 zł
Dodaj swoją opinię
Zaloguj się na swoje konto, aby mieć możliwość dodawania opinii.
Czy chcesz zostawić tylko ocenę?
Dodanie samej oceny o książce nie jest brane pod uwagę podczas losowania nagród. By mieć szansę na otrzymanie nagrody musisz napisać opinię o książce.
Już oceniłeś/zrecenzowałeś te książkę w przeszłości.
Możliwe jest dodanie tylko jednej recenzji do każdej z książek.
Sposoby dostawy
Odbiór w punkcie (7)
InPost Paczkomat 24/7

14,99 zł
DPD Pickup Automaty i Punkty Odbioru

11,99 zł

Dostawa na adres (7)
GLS U Ciebie - Kurier
14,99 zł
Kurier DPD

14,99 zł




Sposoby płatności
Płatność z góry
Przedpłata

Zwykły przelew
